iHateReading — software development blogs

iHateReading is a software development learning platform that breaks programming topics into step-by-step threads, roadmaps, templates, and curated developer resources. The homepage lists practical tutorials for React, Next.js, Node.js, JavaScript, TypeScript, AI tooling, and product engineering. Each thread is a short, structured walkthrough you can skim, bookmark, and reuse while building. Use iHateReading when you need a concrete implementation path rather than a long essay: how to add auth, ship a SaaS starter, submit a product to directories, follow a frontend or backend roadmap, or scan GitHub trending repositories. Start from the article index at /blog, or the machine-readable list at /articles.json. Continue to Explore for curated blogs, the Magazine for a monthly developer digest, Roadmaps for skill paths, Store for website templates, Jobs for developer roles, and SaaS Directories for launch lists. Machine-readable index: https://ihatereading.in/llms.txt. Latest articles JSON: https://ihatereading.in/articles.json. RSS: https://ihatereading.in/rss.xml (also /feed.xml). Topics: https://ihatereading.in/topics (e.g. /topics/react). Search: https://ihatereading.in/search?q={query}. Blog sitemap: https://ihatereading.in/sitemap-blogs.xml. Sitemap index: https://ihatereading.in/sitemap_index.xml. About: https://ihatereading.in/about.

Machine-readable index: https://ihatereading.in/llms.txt. XML sitemap: https://ihatereading.in/sitemap.xml. Agent instructions: https://ihatereading.in/agent-instructions.md.

Show previous threadShow next thread

Authentication Using JSON Web Token

Apr 16, 2023
7 steps
min

Copy HTML

Copy Markdown

Authentication Using JSON Web Token cover image

JWT Structure

Header: Contains the details of the token such as the type of algorithm
Payload: Contains the data that need to be authenticated or exchanged securely such as password
Signature — Contains the signature to verify the token or message

Hashing & Salting Passwords

In addition to the first method if the user's email and passwords are correct and the token is generated so before sending the token back to the client store the token in the database.
You can even add salting and hashing to the password it is just a more secure way to store passwords in databases than most databases nowadays do.
Refer bycypt npm module to hash the password and salting is also not rocket science.
It is just like adding a unique string to the hashed password string and storing that salt in the database.
Next time when we access and cross-check the password we need to check the salt also to verify it completely.

2 steps to add JWT security

To secure the application servers we can add JWT layer.
  • The server creates JWT token using user credentials
  • The server then sends JWT back to the client
  • The client sends back JWT to the server to access database or other services
  • The server then decodes JWT using credentials and verify the token validity
  • If the token is valid client is allowed the access otherwise thrown an error
That’s how JWT is used to secure the application.

Conclusion

That’s all about JWT, literally, it contains only 2 steps.
Of course, in the production-based application we need to add more details or more methods in between but the basic overview will remain the same.
I hope you have learned something, don’t forget to subscribe.
Until next time, have a good day, people.
Shrey

Creating Tokens

  • JWT provides a sign method to create a token using credentials
  • Create an endpoint that takes the user email and password as parameters
  • Create a token using an email
  • Send the token back to the client
  • Store the user credentials in the database
router.post('/login', (req, res) => {
 const { email, password }= req.body;
 const token = await jwt.sign({ email });
// store user credentials in DB
// You can even hash the password with salting to make it more secure
 res.send(token)
})

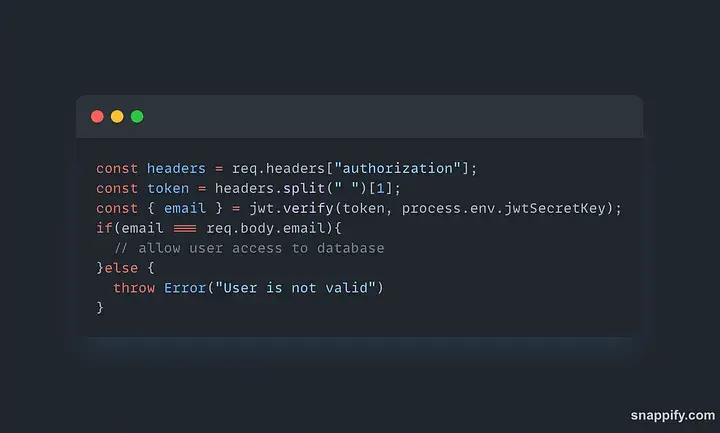
Verifying Tokens

  • Create an endpoint that takes the user email as the parameter and token in the header
  • Use JWT verify method to verify the token sends in the header
  • JWT verify method takes JWT secret key also which is hard coded string and can be anything saved in the env file
  • JWT verification method returns the valid email extracted from the token so match the email with the email send in the API request
  • If the email is the same token is valid otherwise throw an error
router.post('/verify', async(req, res) => {
  const {email} = req.body;
  const header = req.header['Authorization'];
  const token = split(" ")[1];
  const { email: userEmail } = await jwt.verify(token, jwtSecreyKey);
  if(userEmail === email){
    // token is valid
  }else {
     // Invalid token create new token or sends error to the client
  }
  
})
In just 2 steps you can add JWT secure layer and most of the security work is done.

Under the Hood

JWT is encrypted JSON tokens to authenticate and exchange information securely.
I won’t go much into detail about the introduction to JWT, I’ve already covered a story about it so go ahead.

Please login to leave a comment

No comments yet. Be the first to comment!


Subscribe

Our once a week newsletter on Programming, Jobs, AI, and Business